The manufacturer claims it has disabled remote interface modifications and severed external access to its backend systems. According to an unsigned statement, Energize Lab is also purging existing user profiles, conversation logs, and custom avatar images from its servers. While the company insists these measures address the core security failures, the situation remains precarious. Security researcher Sammy Azdoufal reports that he retains SSH access to the devices, and investigators have confirmed that sensitive audio and visual data remain accessible at unprotected public web addresses. Energize Lab maintains that its long-term memory features will stay offline until a third-party review verifies their safety, though the company has not ruled out resuming data collection once its infrastructure is hardened. For now, the promised security upgrades appear to be a work in progress rather than a complete resolution.
Energize Lab Vows Security Audit After Eiliko Robot Vulnerabilities
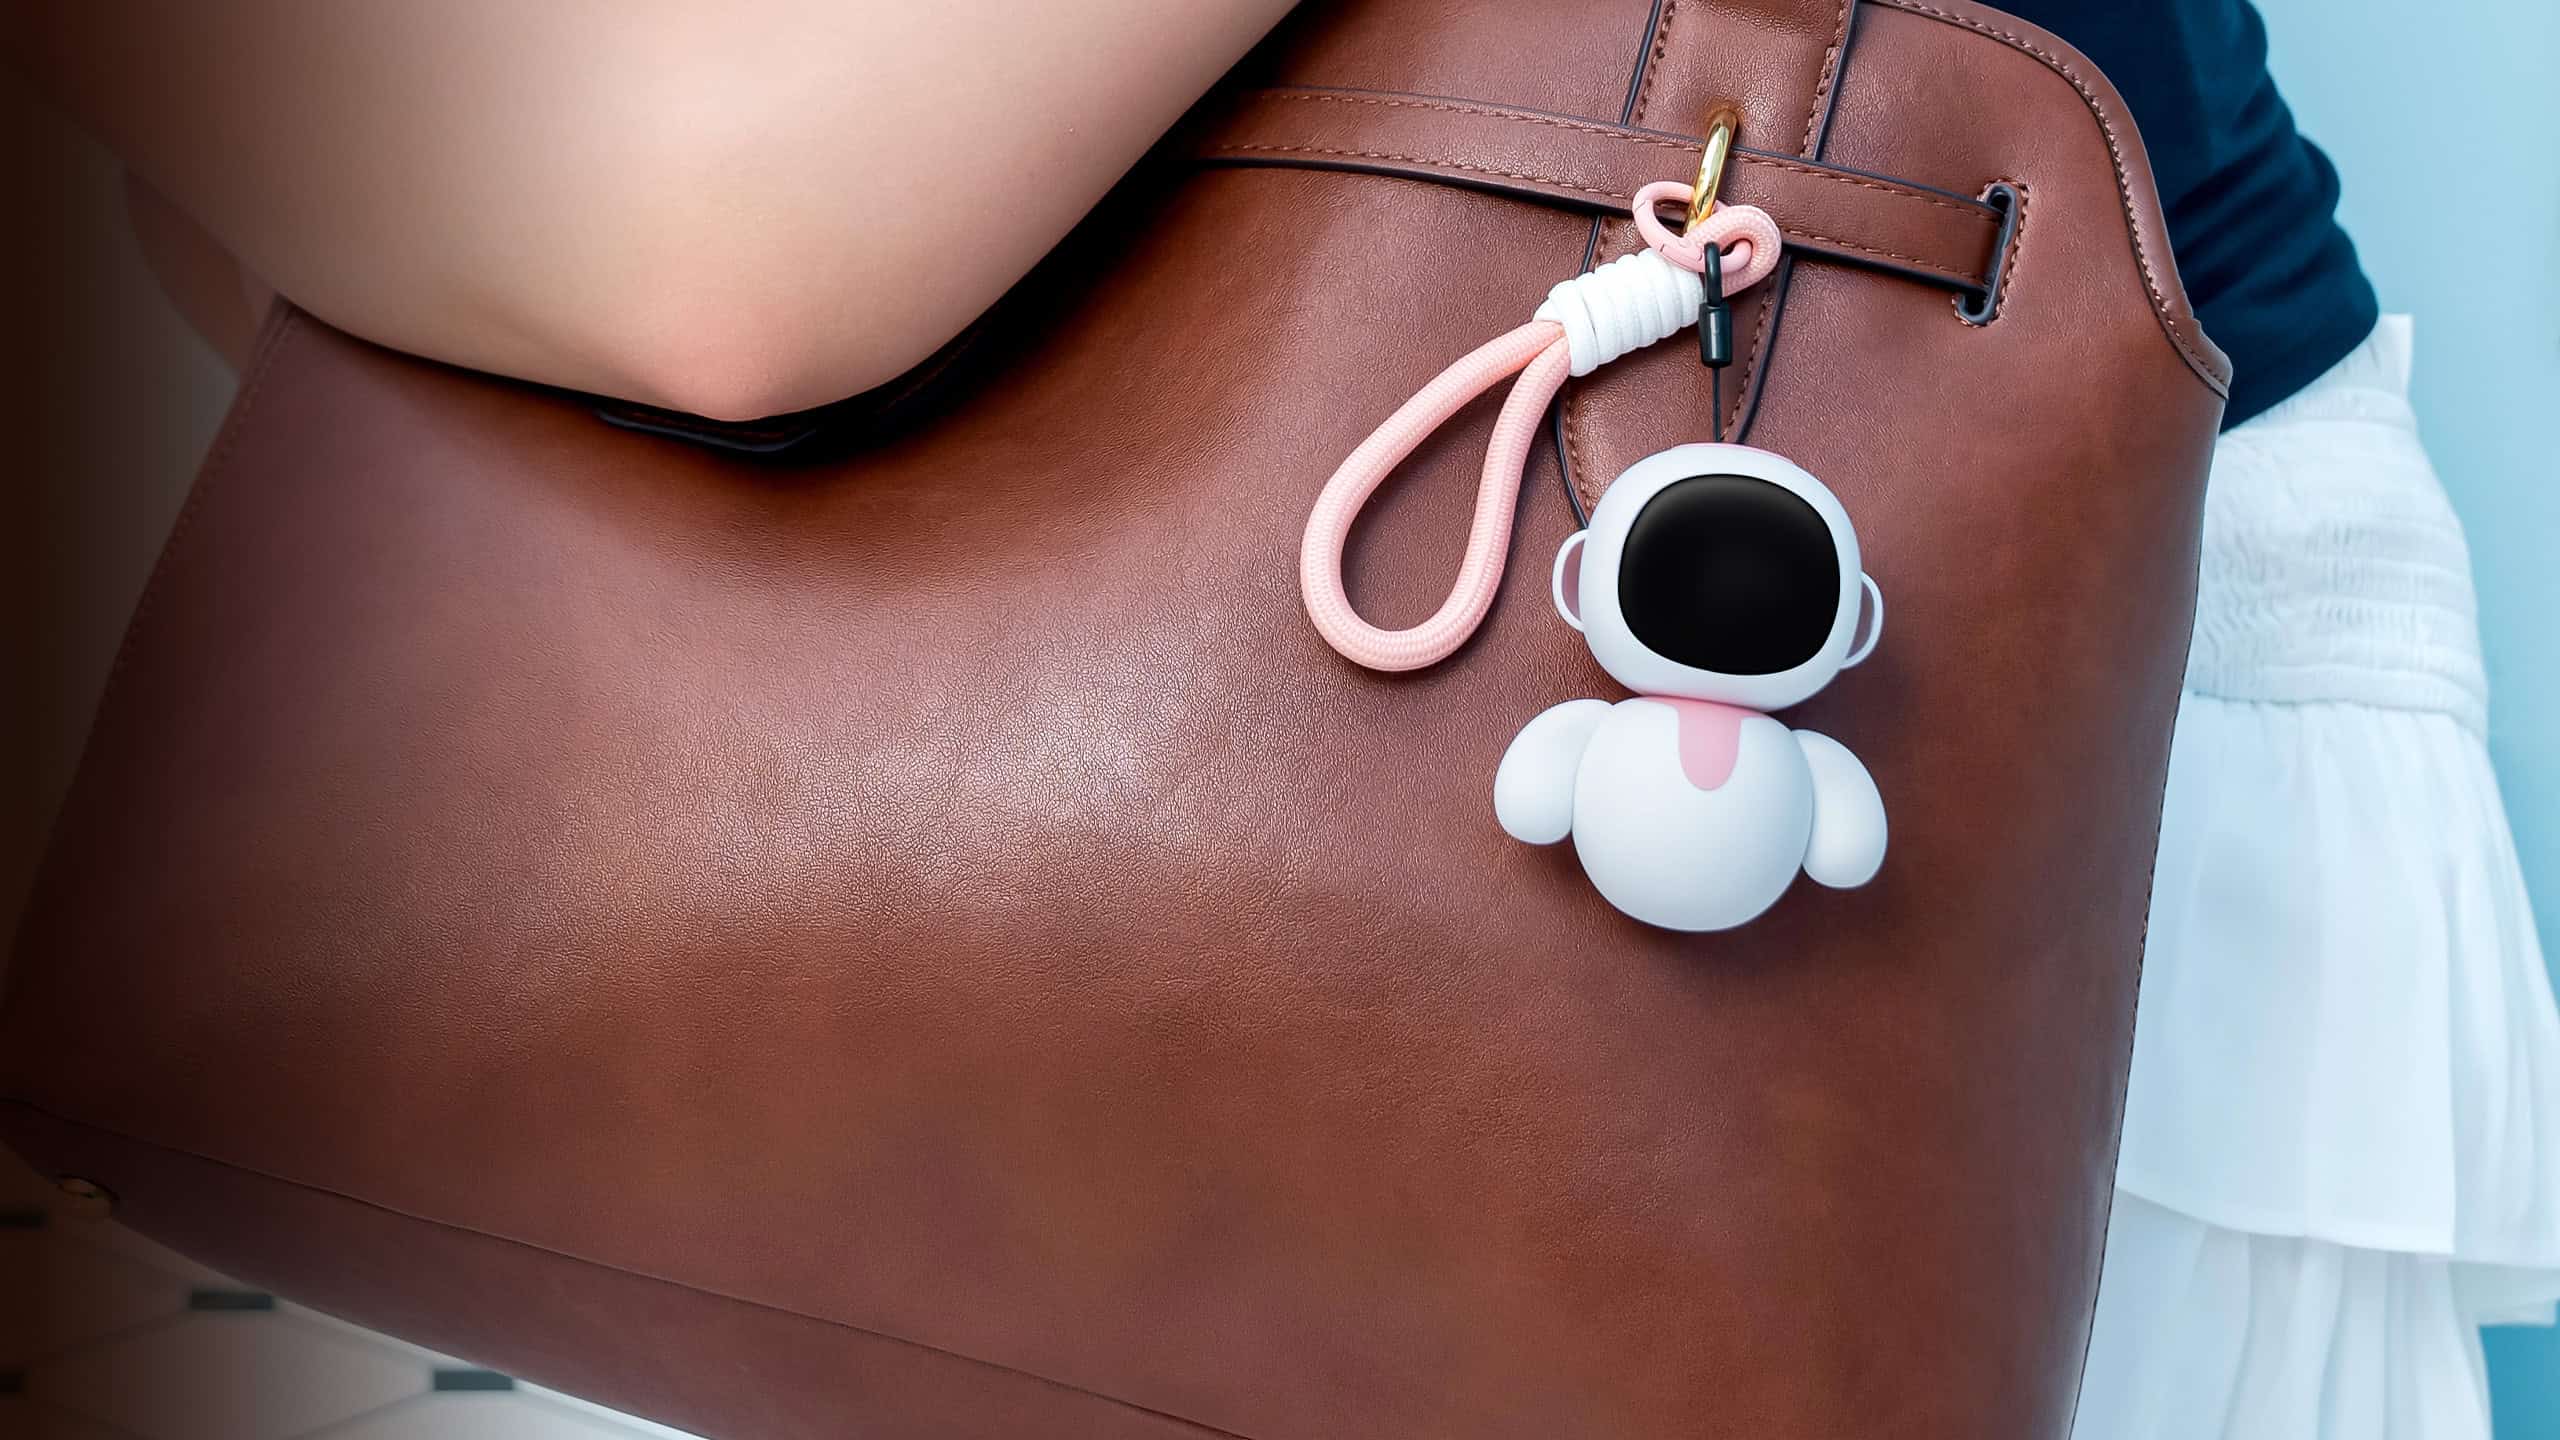
Energize Lab has pledged to hire an independent security firm to audit its Eiliko robot line after investigators revealed the AI-powered charms were leaking private user data. The company’s response follows weeks of silence regarding critical vulnerabilities that allowed unauthorized access to transcripts, audio recordings, and personal photos.


Comments (0)
No comments yet. Be the first!